CSI Linux – Digital Forensics & Security Platform
Bootable 64GB USB 3 • OSINT • Cybersecurity • Incident Response
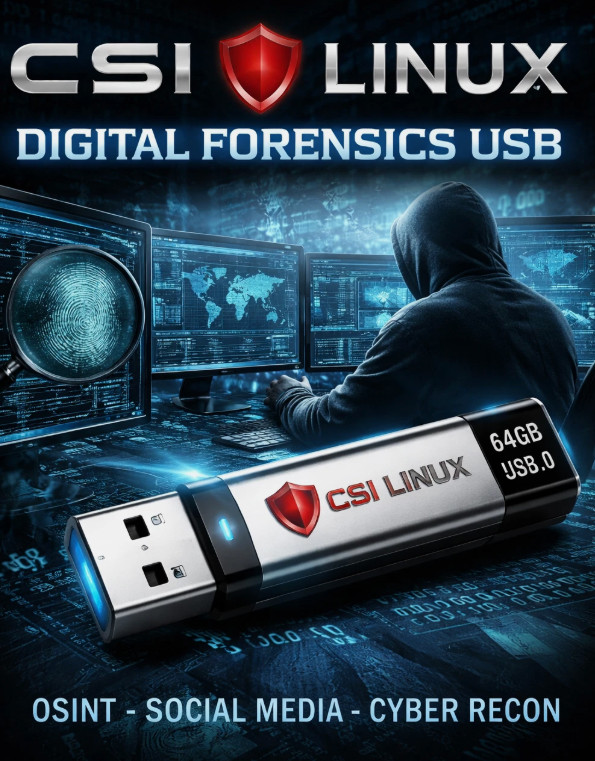
This USB includes CSI Linux, a powerful all-in-one digital forensics and cybersecurity operating system trusted by investigators, analysts, and advanced users. Delivered on a professionally prepared bootable 64GB high-speed USB 3.0 drive, it allows you to run a complete investigation environment without installing anything on the host computer.
CSI Linux combines tools for online investigations and offline forensic analysis, making it a versatile platform for real-world investigative workflows, research, and incident response.
Primary Capabilities • OSINT and open-source intelligence collection
• Social media and username investigations
• Domain and website reconnaissance
• Dark web research and analysis
• Offline digital forensics and evidence review
• Incident response and system triage
• Malware analysis and threat investigation Expanded Tools Core Investigation & Forensics Tools
- Comprehensive CSI investigation tools across multiple forensic disciplines
- Disk image mounting for in-depth forensic examination
- Write-blocking tools to prevent accidental evidence modification
- Evidence hash verification to maintain data integrity
- Timestamped evidence archiving for audit trails and reporting
- Centralized evidence capture with organized, structured storage
OSINT, Recon & Online Investigations
- Advanced domain and website analysis utilities
- Targeted social media feed extraction tools
- Username discovery across social, dark-web, and research platforms
- Geolocation mapping for SSID, BSSID, and IP data
- Specialized investigation browser optimized for OSINT workflows
- Access to publicly available FBI wanted information
Privacy, Anonymity & Dark Web Research
- Secure Tor-based VPN utilities for privacy-focused research
- Custom dark-web research utilities for multiple networks
- Investigator anonymity and operational security tools
- Sock-puppet identity generation for controlled investigative use
Incident Response, Malware & Intelligence
- Incident response triage tools for rapid evidence collection
- Cryptocurrency wallet lookup and transaction analysis tools
- AI-assisted utilities for training and investigative workflows
- A virtual cybersecurity assistant focused on forensic guidance
Usability & Workflow Enhancements
- Custom graphical interfaces integrated with case-management workflows
Features
• Comprehensive CSI investigation tools across multiple forensic disciplines
• Centralized evidence capture with organized, structured storage
• Cryptocurrency wallet lookup and transaction analysis tools
• Secure Tor-based VPN utilities for privacy-focused research
• Custom graphical interfaces integrated with case-management workflows
• Advanced domain and website analysis utilities
• Disk image mounting for in-depth forensic examination
• Write-blocking tools to prevent accidental evidence modification
• Geolocation mapping for SSID, BSSID, and IP data
• Evidence hash verification to maintain data integrity
• Timestamped evidence archiving for audit trails and reporting
• Targeted social media feed extraction tools
• Username discovery across social, dark-web, and research platforms
• Sock-puppet identity generation for controlled investigative use
• Access to publicly available FBI wanted information
• Specialized investigation browser optimized for OSINT workflows
• Investigator anonymity and operational security tools
• Custom dark-web research utilities for multiple networks
• Incident response triage tools for rapid evidence collection
• AI-assisted utilities for training and investigative workflows
• A virtual cybersecurity assistant focused on forensic guidance Use With Confidence
This platform is widely used for cybersecurity research, education, incident response, and digital investigations. All included tools comply with open-source licensing and are prepared, verified, and organized for immediate use.