User # get system central-managementmode: normal
type: enable
schedule-script-restore: enable
allow-push-configuration: enable
allow-pushd-firmware: enable
allow-monitor: 0.0.0.0
fmg-source-ip6: ::
vdom: enable
enc-algorithm: # show system global
config system global
set fgd-alert-subscription advisory latest-threat
set hostname " "
set timezone # show system interface
config system interface
edit "wan1"
set vdom "root"
set mode dhcp
set allowaccess ping fgfm auto-ipsec
set type physical
set snmp-index 2
next
edit "wan2"
set vdom "root"
set allowaccess ping fgfm auto-ipsec
set type physical
set snmp-index 3
next
edit "modem"
set vdom "root"
set mode pppoe
set type physical
set snmp-index 4
next
edit "ssl.root"
set vdom "root"
set type tunnel
set alias "SSL VPN interface"
set snmp-index 5
next
edit "internal"
set vdom "root"
set ip 192.168.1.99 255.255.255.0
set allowaccess ping https ssh http fgfm capwap
set type physical
set snmp-index 1
next
edit "dmz"
set vdom "root"
set type physical
set snmp-index # get system status
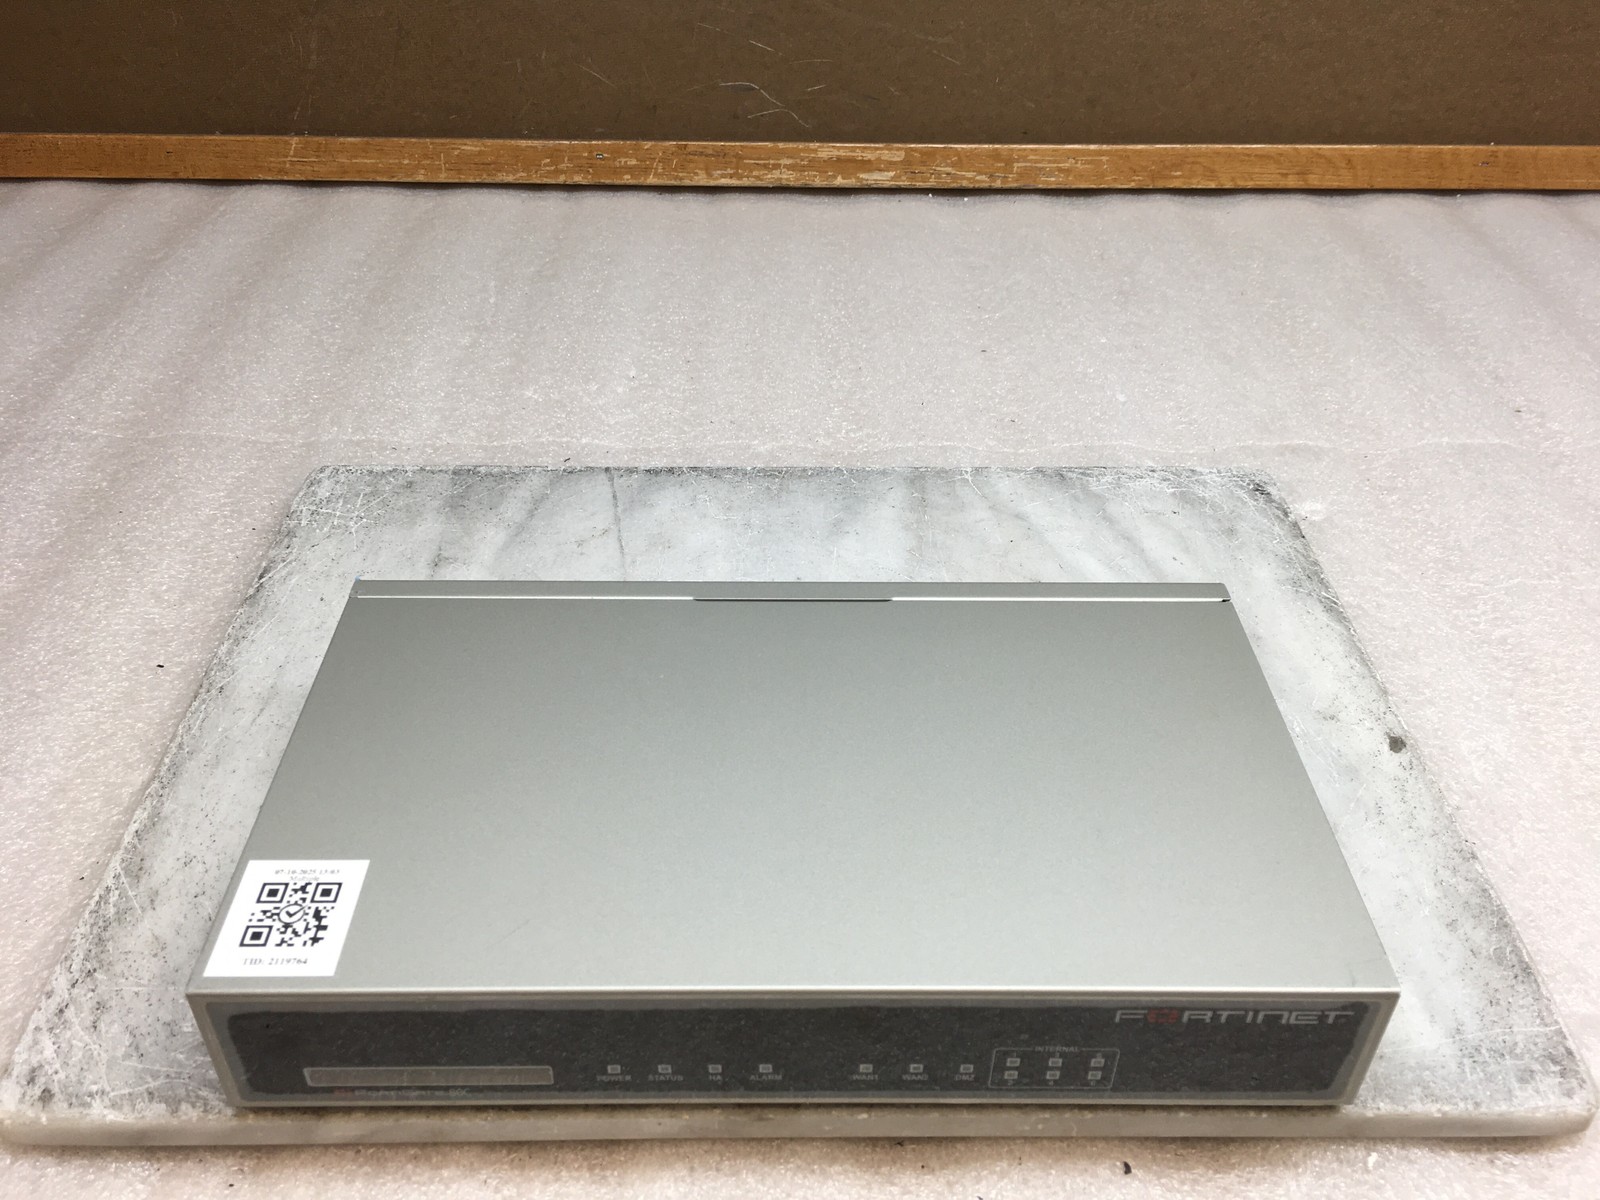
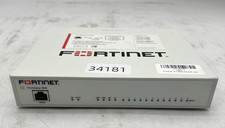
Version: FortiGate-80C v5.2.1,build0618,140915 (GA)
Virus-DB: 61.00520(2018-08-17 01:29)
Extended DB: 23.00160(2014-11-10 09:10)
IPS-DB: 13.00431(2018-08-15 01:44)
IPS-ETDB: 0.00000(2001-01-01 00:00)
Serial-Number: FGT80C3909621680
Botnet DB: 4.00285(2018-08-16 10:00)
BIOS version: 04000004
Log hard disk: Not available
Internal Switch mode: switch
Hostname: FGT80C3909621680
Operation Mode: NAT
Current virtual domain: root
Max number of virtual domains: 10
Virtual domains status: 1 in NAT mode, 0 in TP mode
Virtual domain configuration: disable
FIPS-CC mode: disable
Current HA mode: standalone
Branch point: 618
Release Version Information: GA
System time: Thu Jul 10 09:24:33 # get system performance status
CPU states: 0% user 0% system 0% nice 100% idle
CPU0 states: 0% user 0% system 0% nice 100% idle
Memory states: 36% used
Average network usage: 0 kbps in 1 minute, 0 kbps in 10 minutes, 0 kbps in 30 minutes
Average sessions: 1 sessions in 1 minute, 0 sessions in 10 minutes, 0 sessions in 30 minutes
Average session setup rate: 0 sessions per second in last 1 minute, 0 sessions per second in last 10 minutes, 0 sessions per second in last 30 minutes
Virus caught: 0 total in 1 minute
IPS attacks blocked: 0 total in 1 minute
Uptime: 0 days,0 hours,6 # get system global
admin-concurrent: enable
admin-console-timeout: 0
admin-https-pki-required: disable
admin-https-redirect: enable
admin-lockout-duration: 60
admin-lockout-threshold: 3
admin-login-max: 100
admin-maintainer: enable
admin-port: 80
admin-scp: disable
admin-server-cert: self-sign
admin-sport: 443
admin-ssh-grace-time: 120
admin-ssh-port: 22
admin-ssh-v1: disable
admin-telnet-port: 23
admintimeout: 5
allow-traffic-redirect: enable
anti-replay: strict
arp-max-entry: 0
auth-cert: self-sign
auth-http-port: 1000
auth-https-port: 1003
auth-keepalive: disable
av-failopen: pass
av-failopen-session : disable
batch-cmdb: enable
block-session-timer : 30
br-fdb-max-entry: 0
cert-chain-max: 8
cfg-save: automatic
check-protocol-header: loose
check-reset-range: disable
clt-cert-req: disable
csr-ca-attribute: enable
daily-restart: disable
dst: 8009
explicit-proxy-auth-timeout: 300
fds-statistics: enable
fgd-alert-subscription: advisory 8010
fortiextender: disable
fortiextender-data-port: 25246
gui-antivirus: enable
gui-ap-profile: enable
gui-application-control: enable
gui-central-nat-table: disable
gui-certificates: disable
gui-custom-language : disable
gui-dhcp-advanced: disable
gui-dlp: disable
gui-dns-database: disable
gui-dynamic-routing : disable
gui-endpoint-control: enable
gui-explicit-proxy: disable
gui-icap: disable
gui-implicit-policy : enable
gui-ips: disable
gui-ipsec-manual-key: disable
gui-ipv6: disable
gui-lines-per-page: 50
gui-load-balance: disable
gui-local-in-policy : disable
gui-multicast-policy: disable
gui-object-tags: disable
gui-policy-based-ipsec: disable
gui-spamfilter: disable
gui-sslvpn-realms: disable
gui-threat-weight: enable
gui-traffic-shaping : enable
gui-utm-monitors: disable
gui-voip-profile: disable
gui-vpn: enable
gui-vulnerability-scan: disable
gui-wan-load-balancing: enable
gui-wanopt-cache: disable
gui-webfilter: enable
gui-webfilter-advanced: disable
gui-wireless-controller: enable
gui-wireless-opensecurity: disable
honor-df: enable
hostname: FGT80C3909621680
http-obfuscate: modified
internal-switch-mode: 1024-25000
ipsec-hmac-offload: enable
ipv6-accept-dad: 1
language: english
ldapconntimeout: 500
lldp-transmission: disable
login-timestamp: disable
management-vdom: root
max-dlpstat-memory: 5
max-report-db-size: 1024
miglogd-children: 0
ndp-max-entry: 0
optimize-ssl: disable
phase1-rekey: enable
policy-auth-concurrent: 0
post-login-banner: disable
pre-login-banner: disable
radius-port: 1812
refresh: 0
registration-notification: enable
remoteauthtimeout: 5
reset-sessionless-tcp: disable
send-pmtu-icmp: enable
special-file-23-support: disable
ssh-cbc-cipher: enable
ssh-hmac-md5: enable
strong-crypto: disable
tcp-halfclose-timer : 120
tcp-halfopen-timer: 10
tcp-option: enable
tcp-timewait-timer: 1
timezone: (GMT-8:00)Pacific tos
traffic-priority-level: medium
two-factor-email-expiry: 60
two-factor-ftm-expiry: 72
two-factor-sms-expiry: 60
udp-idle-timer: 180
usb-wan-auth-type: disable
user-server-cert: self-sign
vdom-admin: disable
vip-arp-range: enable
wifi-ca-certificate : PositiveSSL_CA
wifi-certificate: Fortinet_Wifi
wimax-4g-usb: disable
wireless-controller : enable
wireless-controller-port: 5246
fds-statistics-period: # get system dns
primary: 208.91.112.53
secondary: ::
ip6-secondary: ::
dns-cache-limit: 5000
dns-cache-ttl: 1800
cache-notfound-responses: disable
source-ip: # show system admin
config system admin
edit "admin"
set accprofile "super_admin"
set vdom # show system global
config system global
set fgd-alert-subscription advisory latest-threat
set hostname "FGT80C3909621680"
set timezone # get router info routing-table all
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
config system dhcp server
edit 1
Specifications Functional Condition:
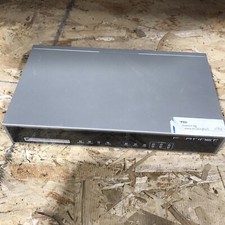
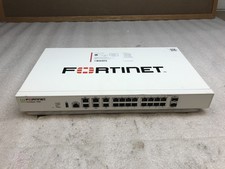
F3 - Key Functions Working Equipment in this category has undergone testing to confirm that its core functionalities are operational. Essential functions that a typical user would expect are verified working. Secondary functions or software may not be present or configured. Units may be missing components or parts that are not essential to key functions.
Cosmetic Condition:
C4 - Used Good Good overall used condition. Some light scratches or scuffs. No dents, dings or cracks.
Data Sanitization:
S3 - Data Clear Device has been sanitized by one of the following methods: Factory Reset, NIST 800-88 Clear, or DOD 5220.22
Mpn
FG-80C Function Tests Powers On
Passed Physical Inspection
Passed Functions
Passed Buttons
Passed Shipping
Tracking information is automatically uploaded to once your order ships.
We ship orders within the contiguous US with FedEx or USPS at our discretion. We use 's shipping calculator for all shipping rates.
PO Box, HI, AK, APO/FPO/DPO, and PR orders must be shipped via USPS. Please contact us or request an adjusted invoice before checking out. Local Pickup
If you have purchased an item and prefer to pick it up, please select “Local Pickup” from the shipping options during checkout. Then please contact us to arrange pickup.
Payment must be made through prior to pickup. Combined Shipping
We can typically provide a 30% shipping discount for multiple purchases that will fit in the same box.
For combined shipping, please click 'Request Total' or send us a message before checking out.
We can then adjust your invoice for combined shipping. Expedited Shipping
In order to guarantee the rates and transit times shown, we must receive your order with its payment cleared by 12:00 PM EST during business days.
Orders placed after 12:00 PM EST will be shipped on the next business day.
Orders placed on weekends or holidays will be shipped the next business day.
Please plan your orders accordingly.
Returns
We strive to be a 5 star seller and hope that you are happy with your purchase.
If there is a problem with your order, please contact us through messages or by phone before leaving response. For items that are tested and working properly:
Our return window for working items listed as "New" or "Used" is 30 days.
If the item is no longer wanted or does not fit, the buyer is responsible for return shipping.
If the item is not working as described, we will work with you on the issue, please contact us to resolve. Please review all product details and sale terms before making a purchase.